Nine ways the Pentagon can fix CMMC without lowering the cybersecurity bar – Federal News Network
Nine ways the Pentagon can fix CMMC without lowering the cybersecurity bar Federal News Network
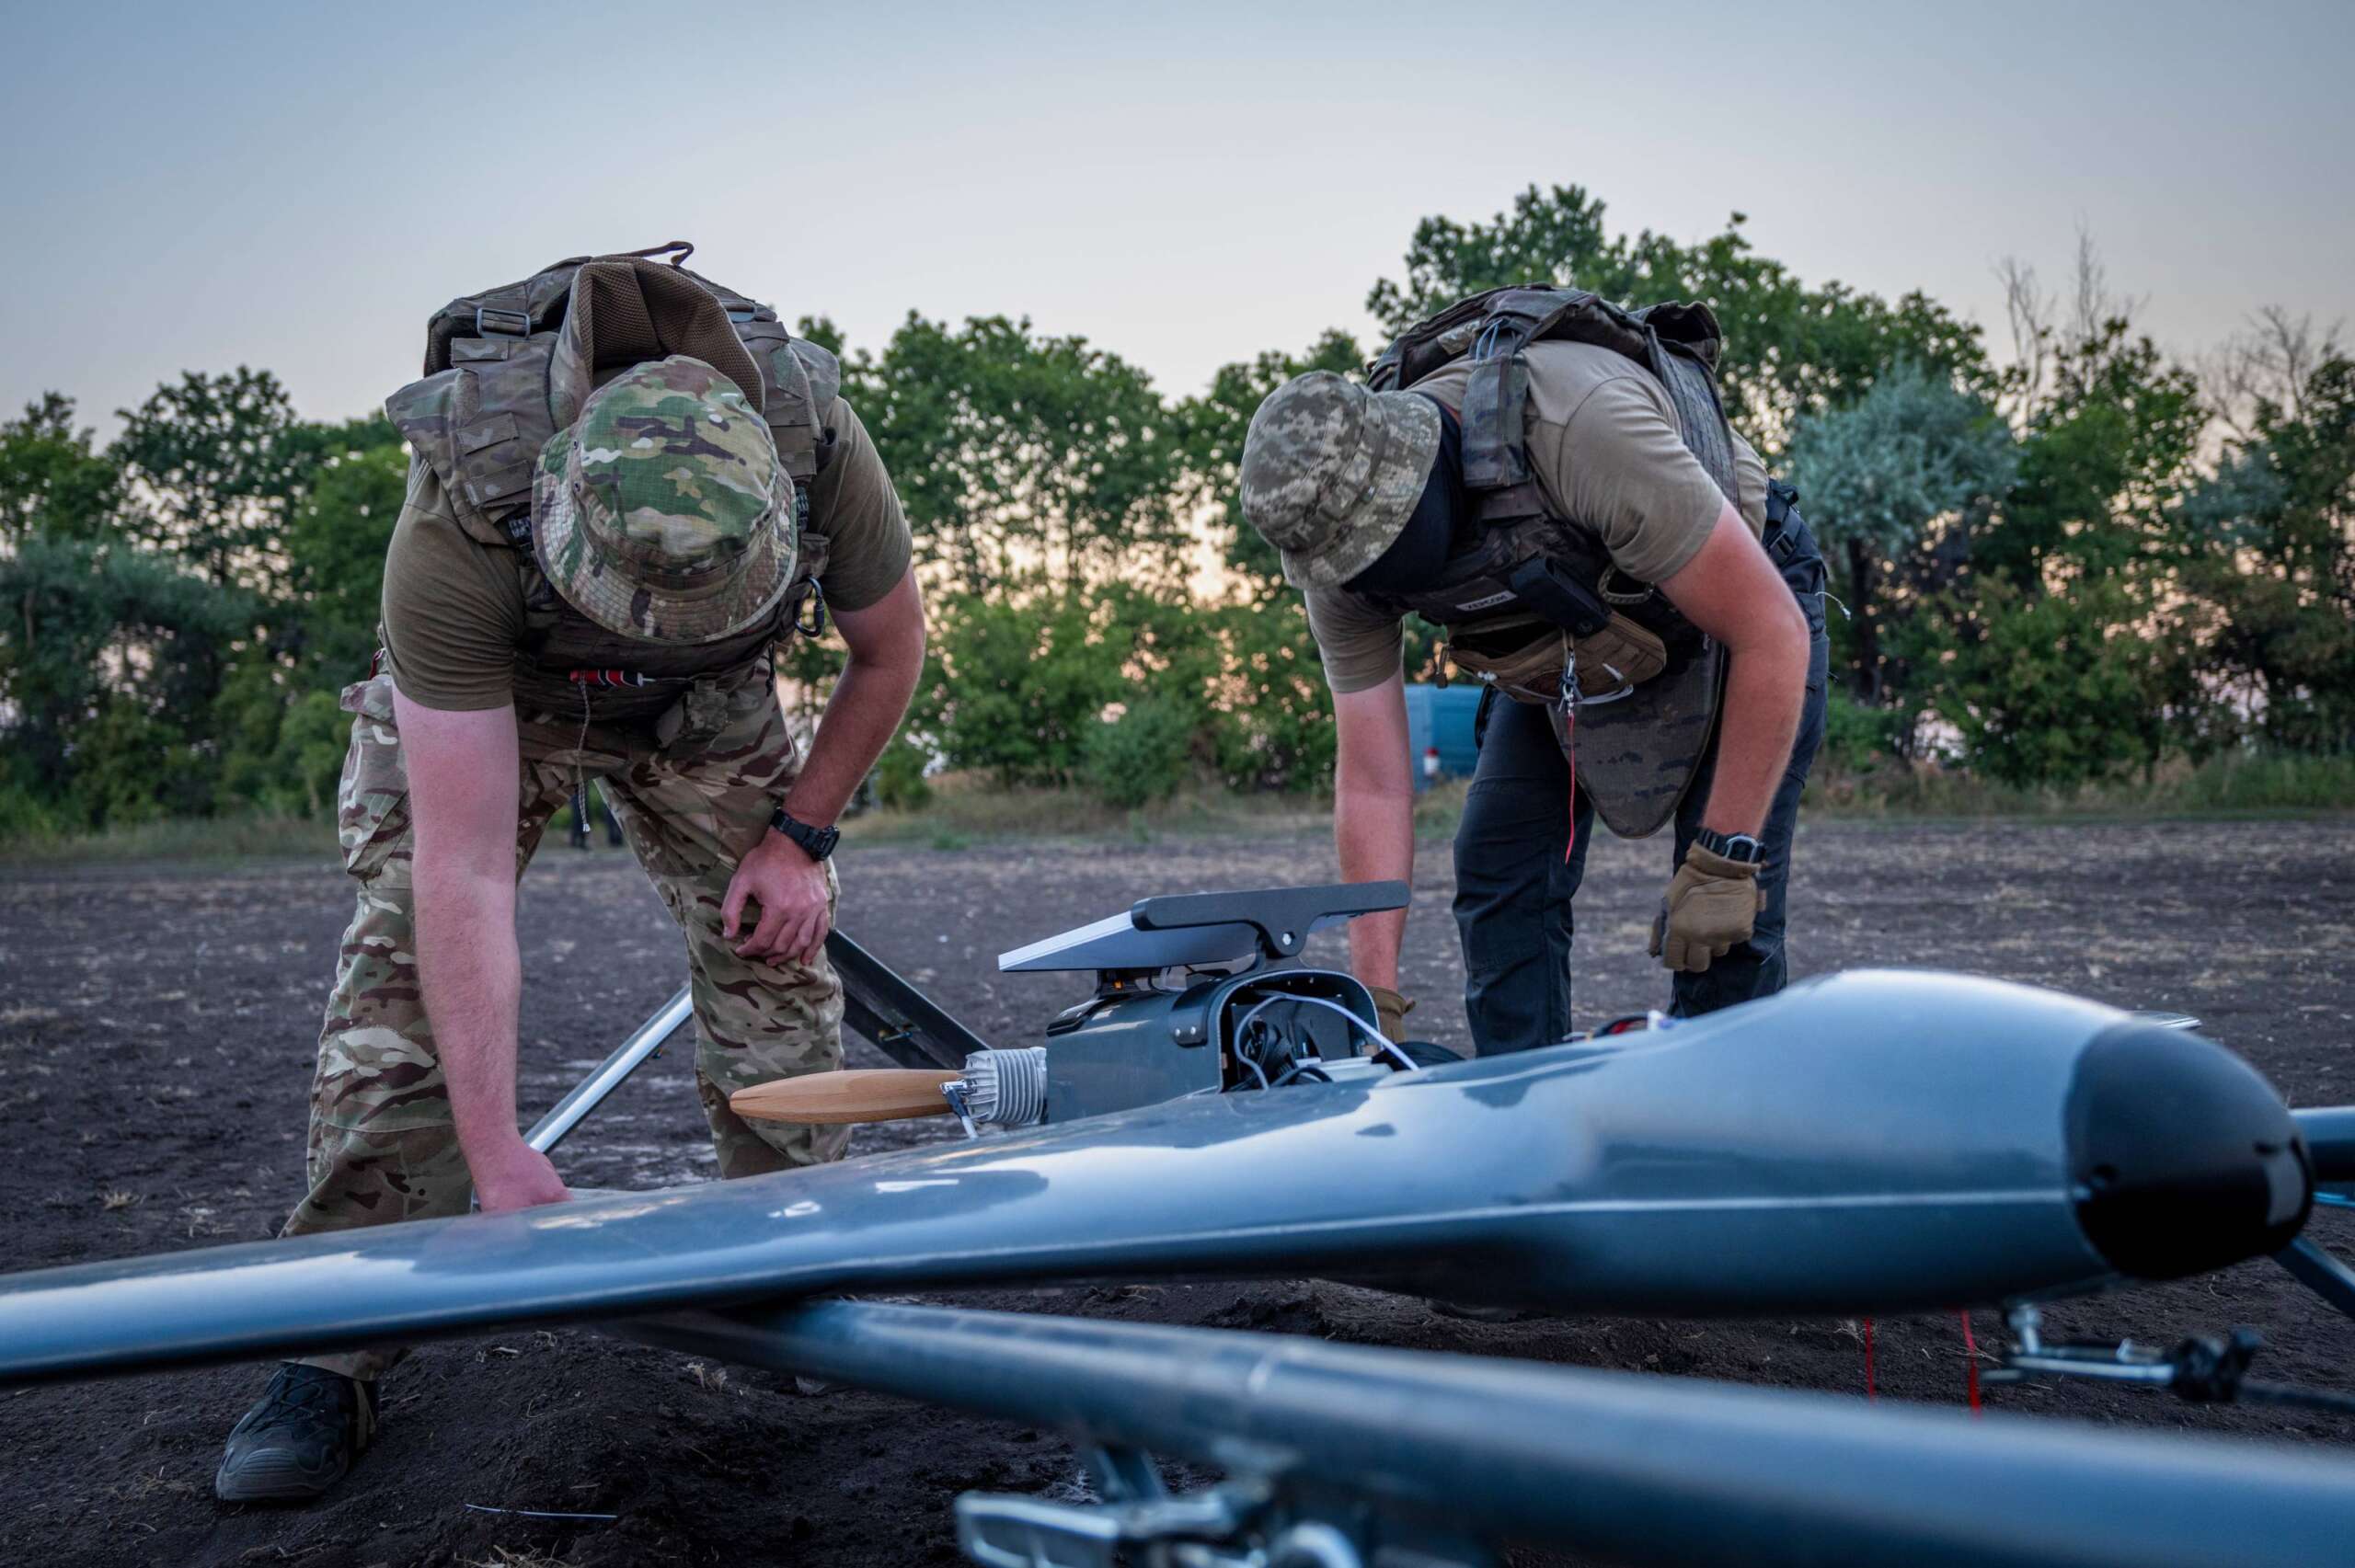
Russia and Ukraine are already demonstrating how quickly AI, autonomous systems, and software can move from development to operational use. The Pentagon should not have to choose between strong cybersecurity and an affordable defense industrial base (DIB). But today, the cost and complexity of complying with the Cybersecurity Maturity Model Certification (CMMC) can put those goals at odds. That tension is becoming more urgent because the battlefield is changing faster than the systems designed to protect it. Consider what happened in Ukraine this summer. On July 6, a Russian drone struck a gas station in Zaporizhzhia in what was described as the first recorded use of a fully autonomous artificial intelligence-powered Russian attack drone.
The drone reportedly used an onboard NVIDIA computer to identify a programmed target and direct itself to strike it. At the same time, Russia and Ukraine are developing broader AI-enabled battlefield systems that can process data from sensors, map targets, and coordinate attacks in minutes. This is the pace of modern warfare. Technology that was experimental yesterday can be deployed on the battlefield tomorrow. Ukraine’s Ministry of Defence reported in September that the number of successful strikes using AI guidance had increased tenfold since the beginning of the year, while both sides continue developing autonomous systems for increasingly complex missions. What are the priorities shaping cybersecurity
Source & Attribution
This One Place News story was acquired from news.google.com. OPN retains the source link and provenance for newsroom review.
Filed Under
Military News