Risk Management Framework as a Service supports Army readiness
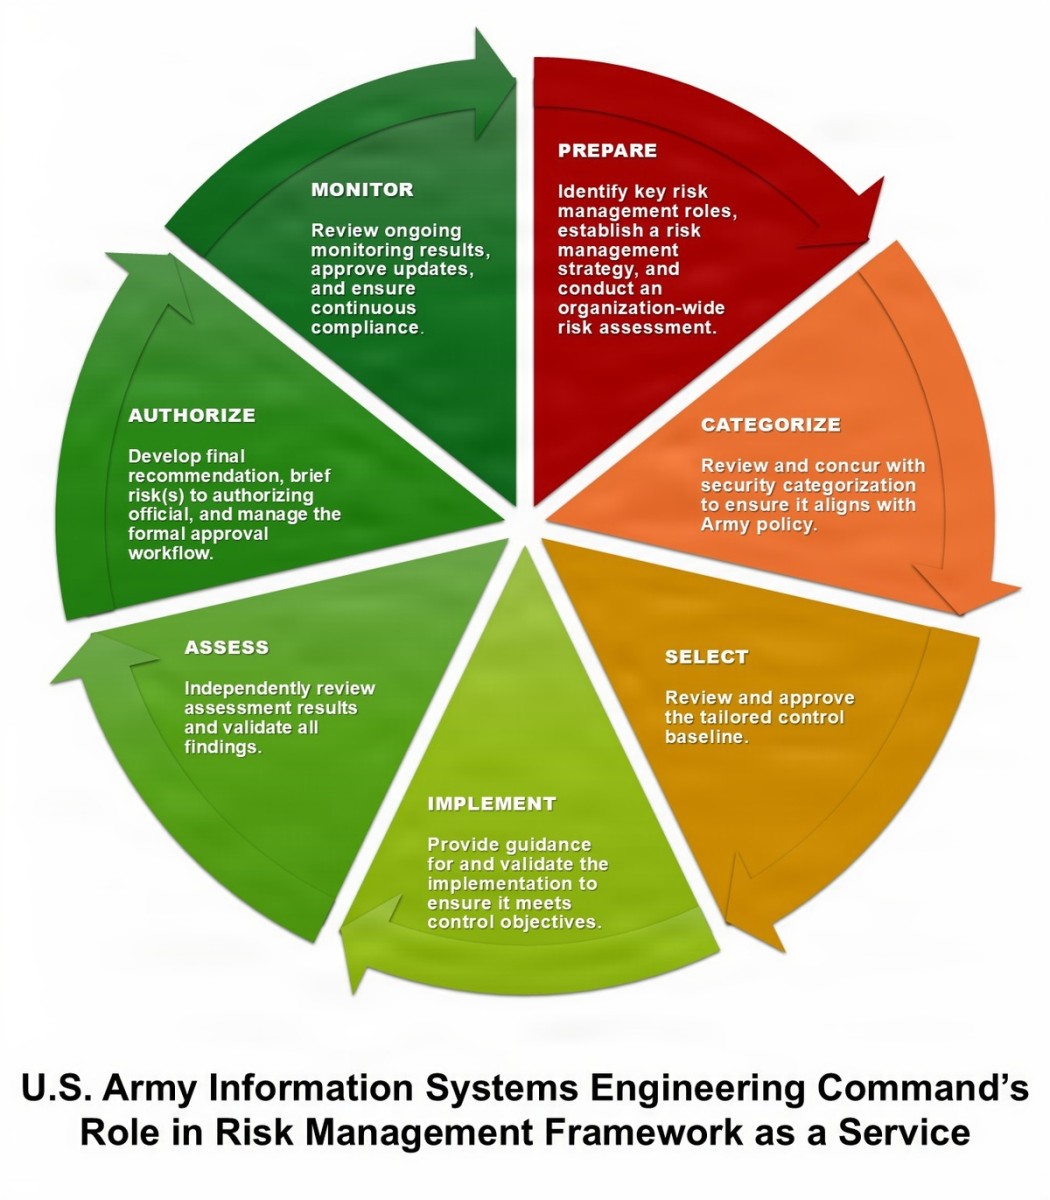
The RMFaaS model delivers specialized cybersecurity expertise directly at the point of need, customized to each organization's distinct operational tempo. FORT HUACHUCA, Ariz. — For more than two decades, the Communications-Electronics Command’s U.S. Army Information Systems Engineering Command has supported Army cybersecurity engineering. During this time, USAISEC has drawn on extensive institutional experience spanning the evolution of legacy security standards from the Department of Defense Information Technology Security Certification and Accreditation Process and the DoD Information Assurance Certification and Accreditation Process to today’s Risk Management Framework. Now, USAISEC is drawing on its comprehensive cybersecurity engineering knowledge to provide an agile RMF as a Service model. The RMFaaS model is designed to support cybersecurity compliance and mission readiness across diverse Department of War systems, directly addressing the growing technical complexity of modern security standards and the shortage of specialized cybersecurity personnel.
To bridge these operational gaps, USAISEC provides dedicated subject matter experts to fill critical compliance roles, such as information system security managers and authorizing official designated representatives, for organizations lacking sufficient organic resources. Across military installations, the RMFaaS model delivers tangible results by securing information and operational technology environments. At the enterprise level, USAISEC provides RMFaaS governance support for the Office of the Provost Marshal General Joint Analytic Real-Time Virtual Information Sharing System. As a web-based security management and threat-tracking
Source & Attribution
This One Place News story was acquired from army.mil. OPN retains the source link and provenance for newsroom review.
Filed Under
Military News